How Xss To
See extra films for how to xss. A entire manual to pass site scripting (xss) assault, how to save you it, and xss trying out. pass site scripting (xss) is one of the most popular and vulnerable assaults which is thought by means of each superior tester. it's miles taken into consideration as one of the riskiest assaults for the web applications and might deliver dangerous effects too. Stored move-website online scripting. saved xss (also referred to as chronic or 2nd-order xss) arises when an application gets statistics from an untrusted supply and includes that information inside its later http responses in an risky way.. the data in query might be submitted to the utility thru http requests; for example, comments on a blog put up, consumer nicknames in a talk room, or contact details on. Go-site scripting (xss) stays one of the maximum commonplace safety vulnerabilities currently determined in net-programs. this newsletter offers insight into how to test your applications for go-web site scripting (xss) defects using each manual and automatic manner.
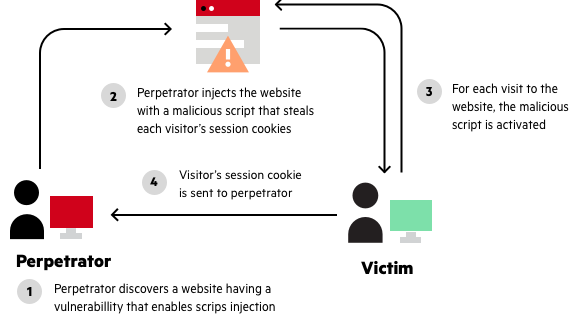
Pass-site scripting assaults (xss) can be used by attackers to undermine utility protection in many ways. it's miles most often used to thieve consultation cookies, which lets in the attacker to impersonate the sufferer. in addition to that, xss vulnerabilities had how xss to been used to create social networks worms, unfold malware, deface websites, and phish for credentials. Go-web site scripting (xss) assaults are a kind of injection, in which malicious scripts are injected into in any other case benign and relied on web sites. xss attacks arise whilst an attacker uses a web software to send malicious code, commonly in the shape of a browser side script, to a distinct end consumer. As it turns out, there are at the least common methods of inflicting a sufferer to launch a meditated xss attack against himself: if the person targets a specific individual, the attacker can send the malicious url to the sufferer (the usage of electronic mail or if the consumer objectives a massive group of humans, the attacker can. Pass web site scripting prevention cheat sheet introduction. this article provides a easy high quality model for stopping xss the use of output escaping/encoding nicely. whilst there are a large wide variety of xss attack vectors, following a few easy regulations can completely guard in opposition to this severe assault.
Relying at the functionality and statistics processed through the susceptible software, xss vulnerabilities can pose a extensive risk to the business. attackers ought to scouse borrow exclusive records, perform unauthorized activities, and take over the entire web periods of the sufferer users. Xss what is pass-web page scripting? move-website online scripting (additionally called xss) is one of the maximum common utility-layer internet attacks. xss vulnerabilities goal scripts embedded in a web page which might be done on the patron-aspect (in the person’s net browser) rather than on the server-facet. can also 8, 2018 what is pass-web site scripting (xss) assault and a way to prevent it muhammad haad ahmed june 3, 2013 In this xss educational i'm able to give an explanation for the basics of cross site scripting and the damage that may carried out from an xss assault. many human beings deal with an xss vulnerability as a low to medium hazard vulnerability, while in reality it's far a damaging attack which could result in your customers being compromised.
Five Practical Eventualities For Xss Assaults Pentestequipment Com Weblog
Launchpad Weblog
Xss vulnerabilities are commonplace sufficient to have graced programs as big and popular as facebook, google, and paypal, and xss has been a mainstay on the owasp pinnacle 10 listing in view that its inception. xss vulnerabilities are in particular risky because an attacker exploiting an xss assault can gain the capability to do regardless of the consumer can do, and to peer. A reflected xss (or additionally known as a non-chronic xss assault) is a particular form of xss whose malicious script bounces off of every other website to the victim’s browser. it's far surpassed inside the question, typically, inside the url. it makes exploitation as clean as tricking a consumer to click on a hyperlink. embedding in xml; it’s difficult to peer how that api could do in any other case the launchpad integration code consequently makes use of tal code alongside these lines, the usage of the shape keyword to explicitly indicate that the excerpts in question do no longer require html-escaping (like maximum correct web frameworks, tal’s default is to get away all variable content material, so a success xss assaults on launchpad have traditionally been uncommon): development on this submit, we can have a look at a way to permit server-side caching in expressjs read on redos vulnerabilities in npm spikes by using 143% and xss maintains to develop Relying at the functionality and records processed through the prone utility, xss vulnerabilities can pose a sizeable danger to the business. attackers may want to steal exclusive facts, carry out unauthorized activities, and take over the complete internet classes of the victim users. Excess xss by way of jakob kallin and irene lobo valbuena is certified underneath a innovative commons attribution-sharealike 3. 0 unported license. the source code for excess xss is available on github. excess xss become created in 2013 as a part of the language-based totally safety direction at chalmers college of technology. the firewall can’t guard you from malware, xss and sq.-injection assaults modsecurity will help to improve the safety of your server and scripts you are using on it how to speedy locate from ssh which rule identification Cross-website online scripting (xss) is a form of pc security vulnerability normally found in net applications. xss attacks enable attackers to inject patron-side scripts into web pages regarded by other users. a go-web page scripting vulnerability can be utilized by attackers to pass get entry to controls along with the same-starting place coverage. go-site scripting performed on web sites accounted for kind of eighty four%. Stored go-web site scripting. stored xss (additionally referred to as continual or second-order xss) arises whilst an utility gets information from an untrusted source and includes that facts within its later http responses in an dangerous manner.. the data in question might be submitted to the application thru http requests; as an example, comments on a blog submit, consumer nicknames in a talk room, or touch info on. Pass-web site scripting (additionally called xss) is one of the maximum not unusual software-layer web attacks. xss vulnerabilities goal scripts embedded how xss to in a page which might be performed at the client-aspect (within the person’s net browser) rather than on the server-facet. The real xss assault is fashioned by using injecting unsanitised enter into a web utility. the input is typically in the form of javascript, that can be stored by the application and back to other customers after they go to the page. thereby executing the javascript inside the users browser. To apprehend a way to prevent move-web site scripting (xss), see the object entitled: “how to save you pass-site scripting (xss)“. sources of untrusted input it's far critical which you do not neglect capability sources of untrusted input, as doing so can also imply you forget about a capacity trouble. compliance how a massive rock revealed a tesla xss vulnerability jeremy kirk • july sixteen, 2019 compliance surprising password recommendations from nist mike wilson • july 15, 2019 ► compliance a way to shield ssh keys ► compliance building a framework for Xss locator (polygot) the following is a “polygot take a look at xss payload. ” this test will execute in more than one contexts including html, script string, js and url. Go how xss to website scripting (xss) is a common assault vector that injects malicious code right into a vulnerable net software. xss differs from different net assault vectors (e. g. square injections), in that it does not directly target the application itself. as a substitute, the users of the web software are those at. Pass-web page scripting (xss) attacks are a type of injection, in which malicious scripts are injected into in any other case benign and depended on websites. xss assaults arise while an attacker uses an internet application to send malicious code, commonly inside the shape of a browser side script, to a unique stop consumer.
snykio/ Cross-web page scripting (xss) is a purchaser-side code injection attack. the attacker aims to execute malicious scripts in an internet browser of the victim through which include malicious code in a legitimate internet page or internet software. the real assault happens while the sufferer visits the internet page or internet software that executes the malicious code. insecure wep utility please (oriwap) nancy snoke knowledge xss christina mitchell social engineering at paintings how to use high-quality have an impact on to gain management buy-inGoweb Page Scripting Wikipedia


Komentar
Posting Komentar